Website security compliance remediation CMMC readiness context Evidence for assessments

CMMC website compliance remediation
readiness case snapshot

This mini case page explains how CMMC website compliance remediation typically works: you identify readiness gaps, we translate them into an actionable punch list at the website and hosting layer, then we implement verifiable fixes so your team can document progress and reduce assessment friction.

Website hardening
TLS and headers
DNS and protocols
Evidence ready
Home> Website Services> Website Security and Compliance Remediation> CMMC Website Compliance Remediation
1What readiness teams care about

Website and hosting findings that create compliance friction

For contractors and suppliers, readiness often breaks down on the details. Public websites can expose software versions, weak transport settings, missing security headers, and misaligned DNS and email protocols. That is where CMMC website compliance remediation helps. We focus on fast, verifiable improvements at the website and hosting layer that reduce noise in assessments and tighten your external posture.

Primary goal
Reduce exposure
Lower information disclosure and eliminate avoidable red flags from public scan data.
Operational goal
No disruption
Apply changes with minimal downtime and clear rollback paths when needed.
Documentation goal
Evidence ready
Provide a clean record of what changed so your team can capture and retain proof.
2Audit-to-action workflow

From gap list to verifiable remediation

Your cybersecurity team drives the program. We support the execution at the website and hosting layer and focus on outcomes that can be rechecked and documented.

1. Identify external signals

Review scan results, vendor tooling, and public posture indicators that can affect readiness and trust.

Exposure points Scan noise Risk prioritization

2. Translate into a punch list

Turn findings into a sequence of actions that are safe to deploy and easy to validate.

Sequencing Dependencies Rollback plan

3. Remediate and harden

Patch, harden, reduce disclosure, strengthen transport and headers, and align DNS and email protocols.

Patch management TLS and headers DNS and DMARC

4. Verify and document

Recheck results, capture evidence, and produce a concise summary your team can retain.

Verification Evidence trail Assessment support
3Visual snapshots

Readiness style views that match the context

Two visuals that support the story: what was identified, then what was remediated and how it can be verified.
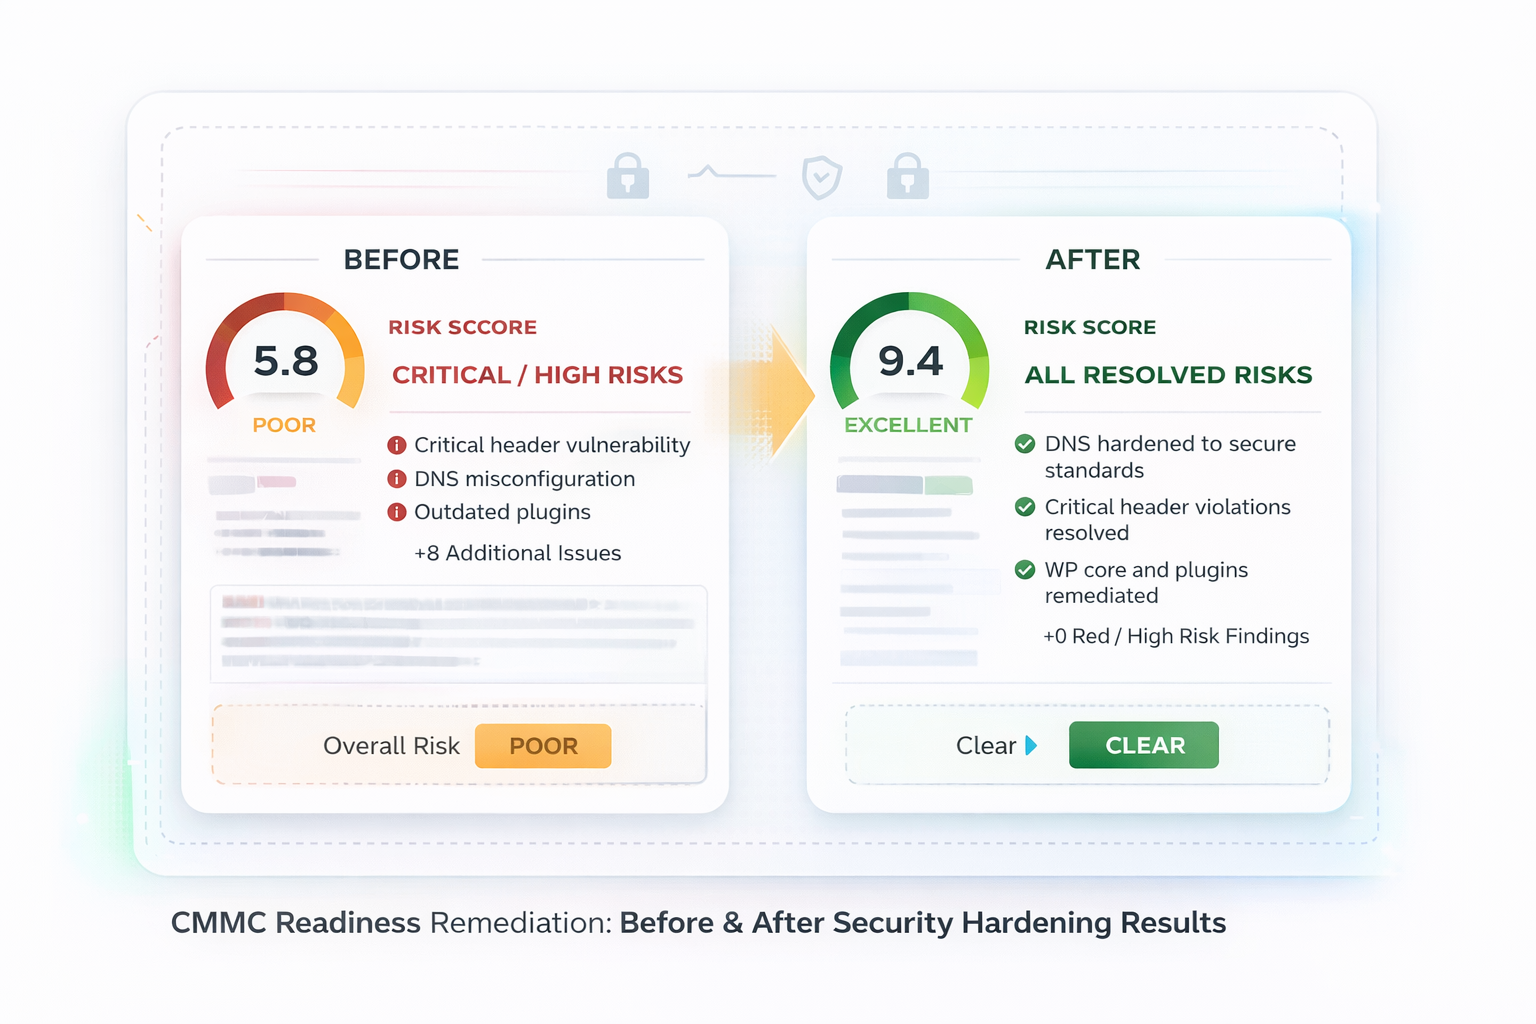
Snapshot A CMMC readiness view
Gap context
CMMC website compliance remediation readiness snapshot visual
A readiness style view that communicates exposure reduction and a clear remediation direction.
Snapshot B Verification and remediation view
Evidence context
CMMC website compliance remediation verification summary visual
A summary style view showing that changes can be rechecked and documented by your internal team.
4Frequently asked questions

CMMC readiness and what we remediate on the website layer

These answers clarify scope and reduce confusion about who owns what in a compliance program.

It means reducing avoidable exposure and tightening security posture where your public site intersects with risk: patch management, transport configuration, security headers, DNS and email protocols, and information disclosure items. For a broader view, see the security and compliance remediation hub.
No. They drive governance, controls, and verification. We remediate at the website and hosting layer and provide a clear list of what changed so your team can capture evidence and reduce remediation backlog.
Updating software safely, eliminating risky or outdated components, strengthening TLS configuration, applying security headers, reducing information leakage, and aligning DNS and email protocols such as SPF, DKIM, and DMARC.
Send what you have. We can translate partial findings into a practical remediation plan and identify the next information needed to complete the punch list. If you are dealing with insurance scans, also see cyber insurance website risk remediation.
Need a remediation plan you can document? Send your readiness notes and we will respond with a structured punch list focused on the website and hosting layer. You can also review the main hub for related compliance paths.

Related service page: Cyber Insurance Website Risk Remediation. If you want the underwriting example, see Underwriting Case Snapshot.